{"cve":"CVE-2024-26152","nvd":{"published":"2024-02-22T22:15:47.310","modified":"2026-06-17T07:17:12.570","status":"Analyzed","description":"### Summary\nOn all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.\n\n### Details\nNeed permission to use the \"data import\" function. This was reproduced on Label Studio 1.10.1.\n\n### PoC\n\n1. Create a project.\n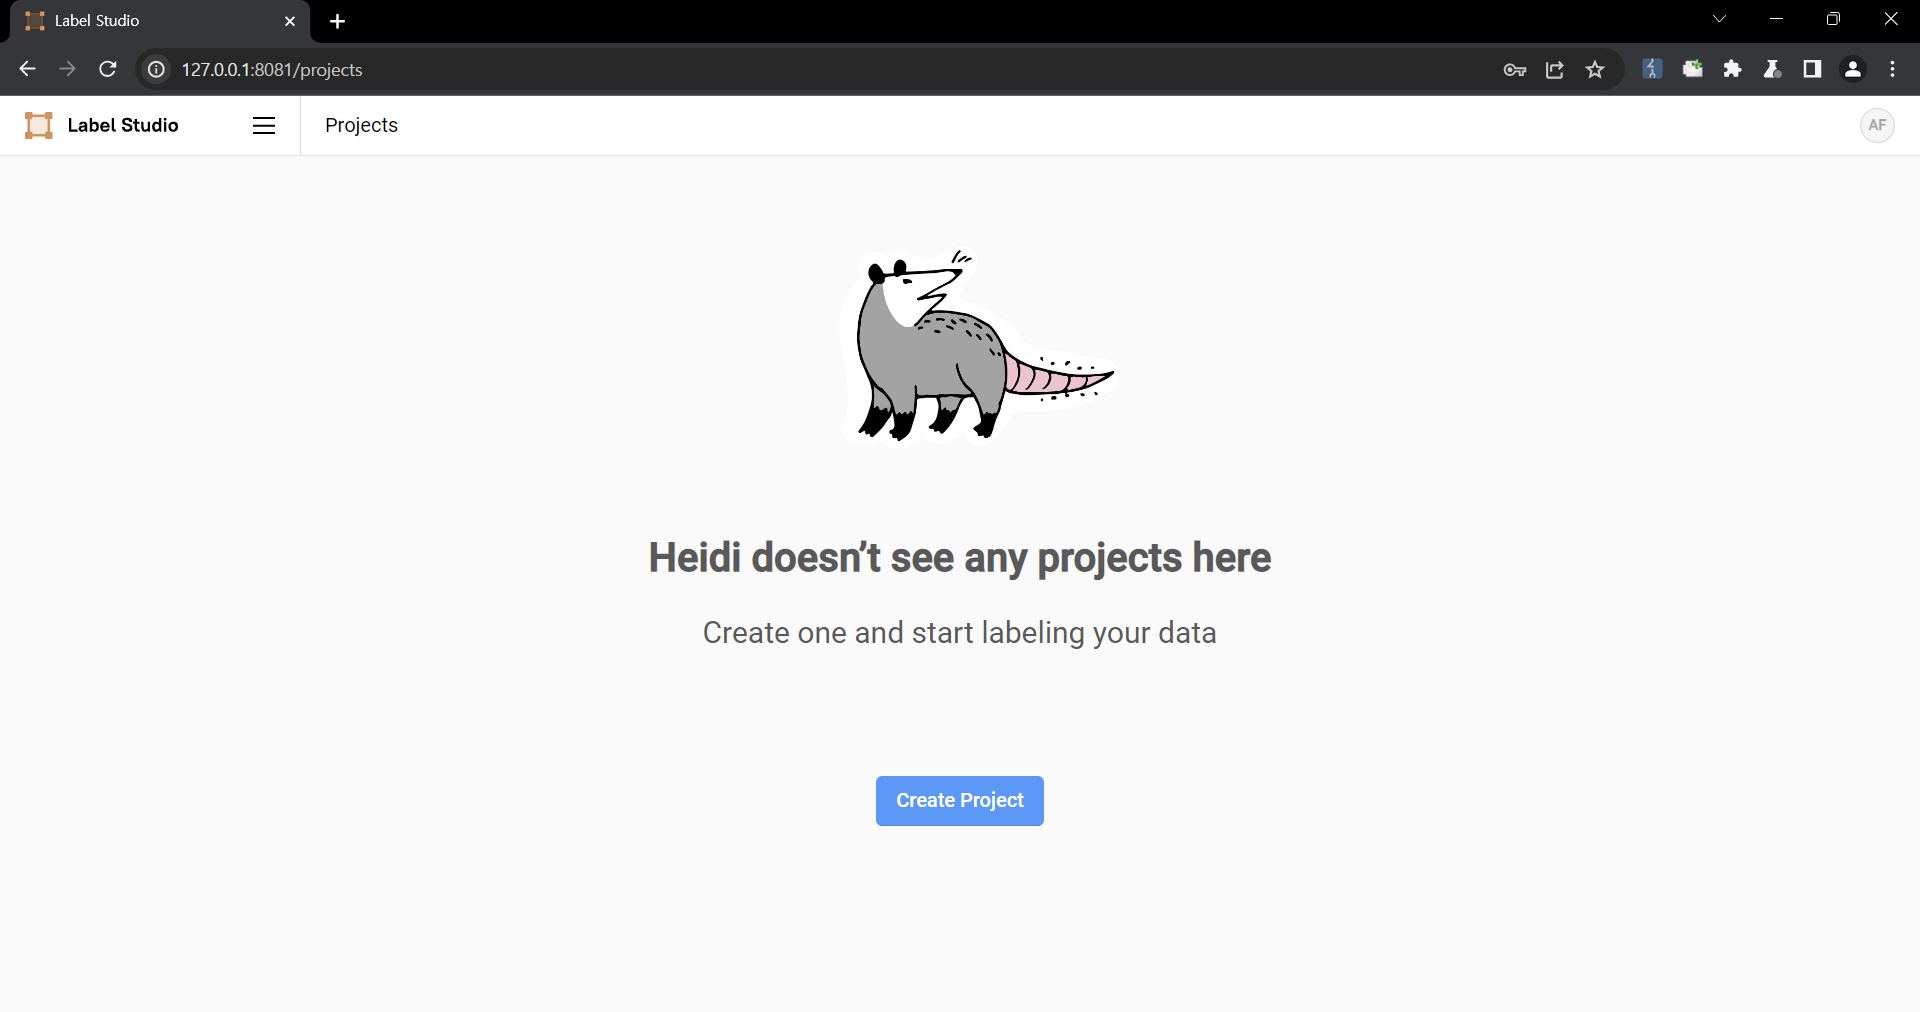\n\n2. Upload a file containing the payload using the \"Upload Files\" function.\n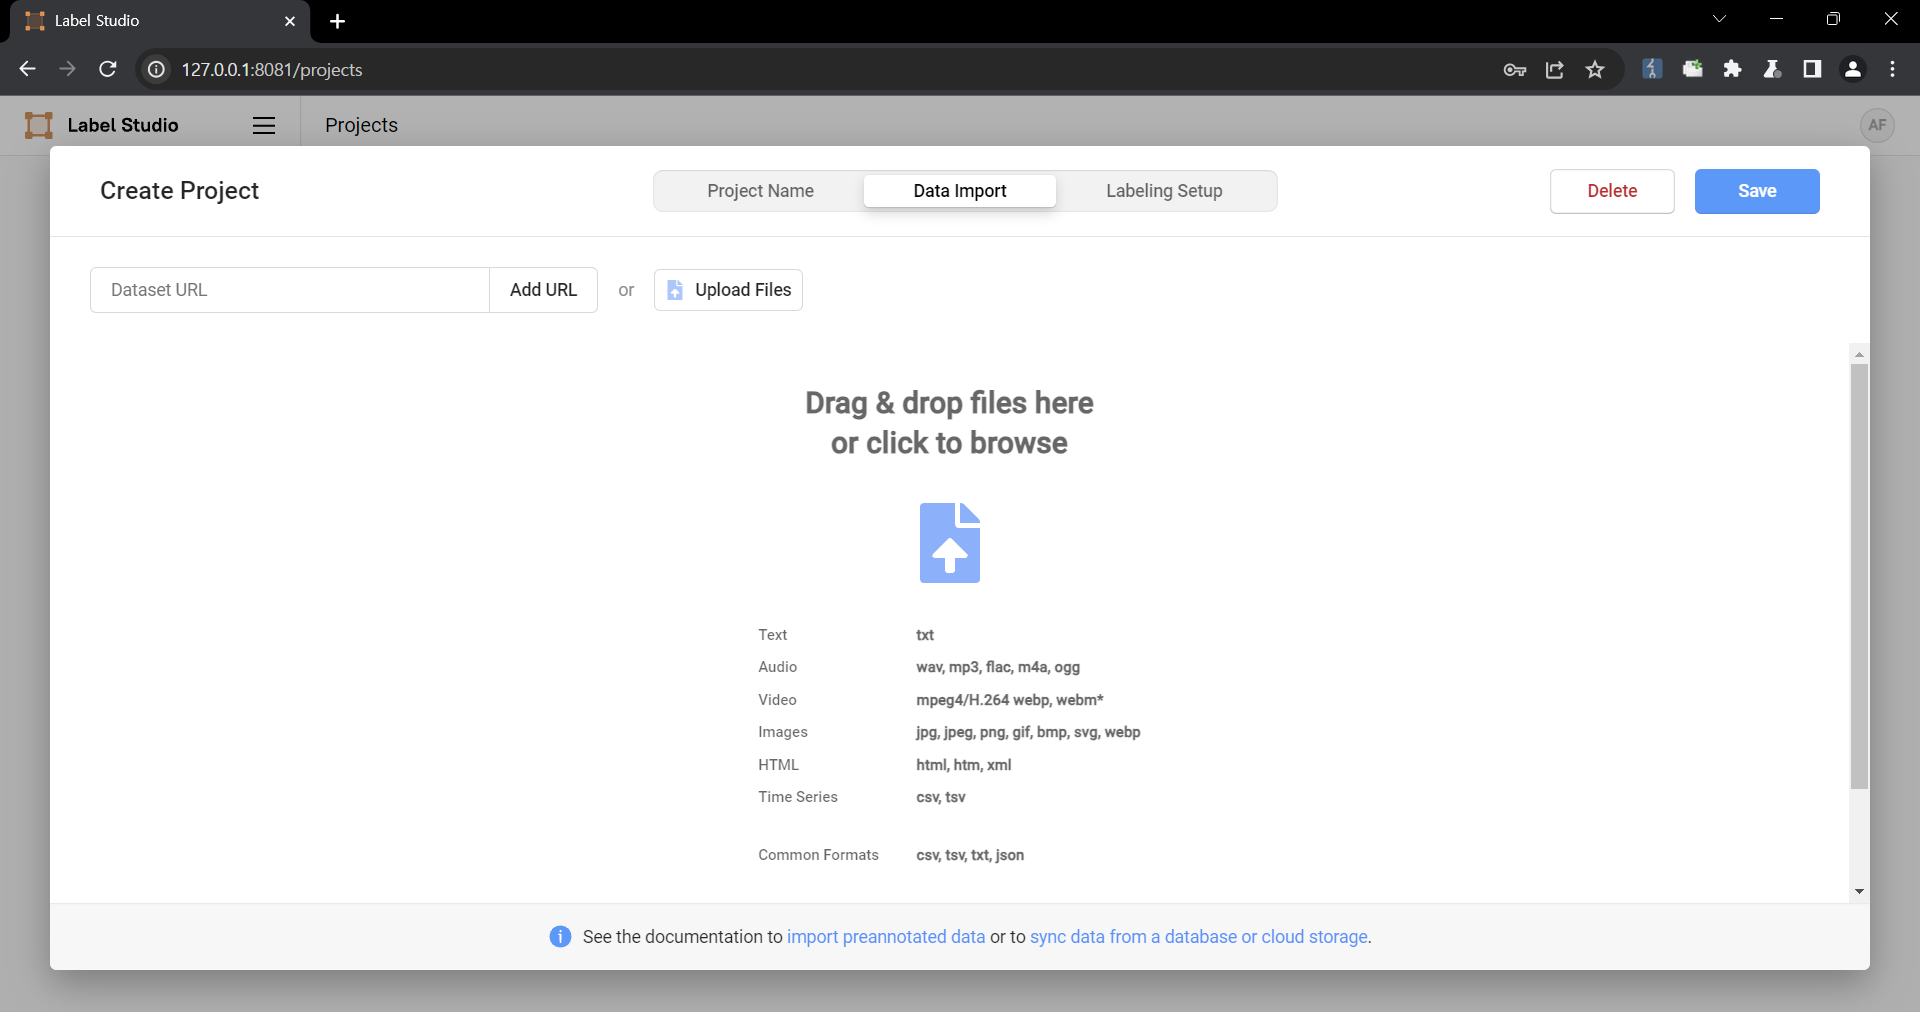\n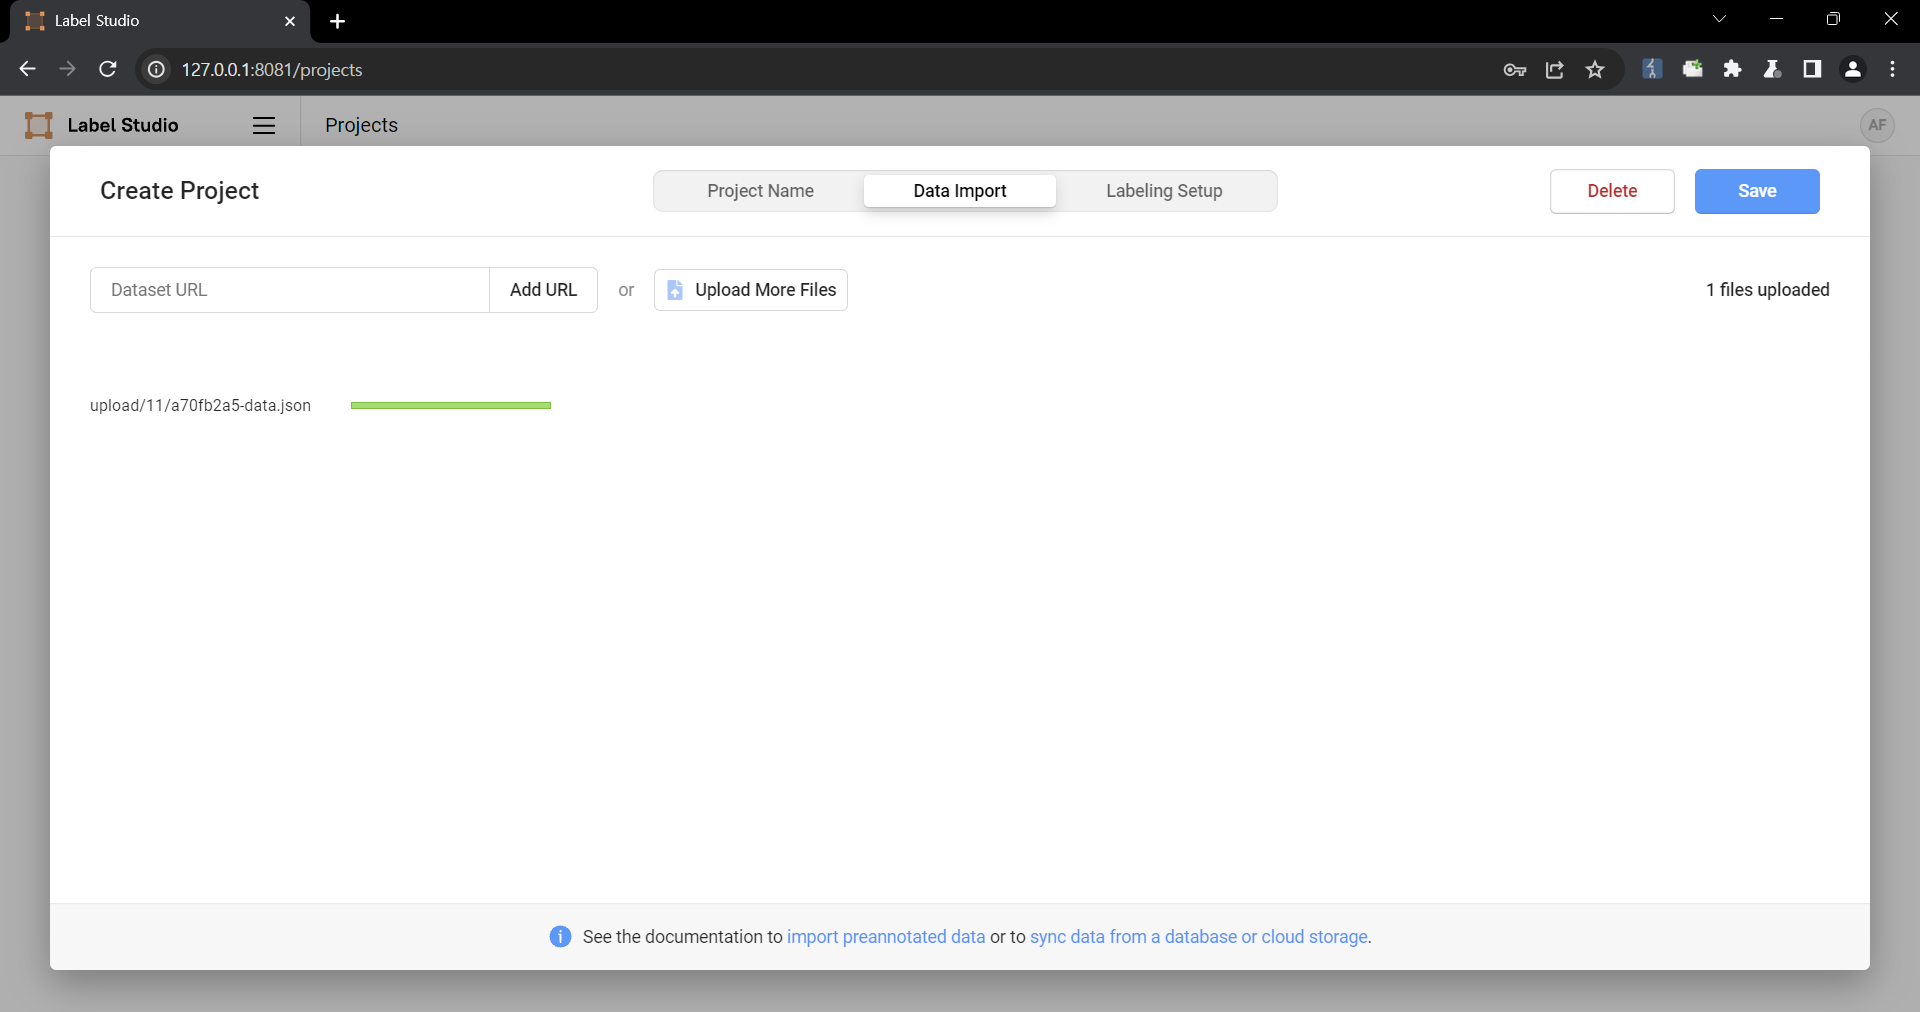\n\nThe following are the contents of the files used in the PoC\n```\n{\n \"data\": {\n \"prompt\": \"labelstudio universe image\",\n \"images\": [\n {\n \"value\": \"id123#0\",\n \"style\": \"margin: 5px\",\n \"html\": \" \"\n }\n ]\n }\n}\n```\n\n3. Select the text-to-image generation labeling template of Ranking and scoring\n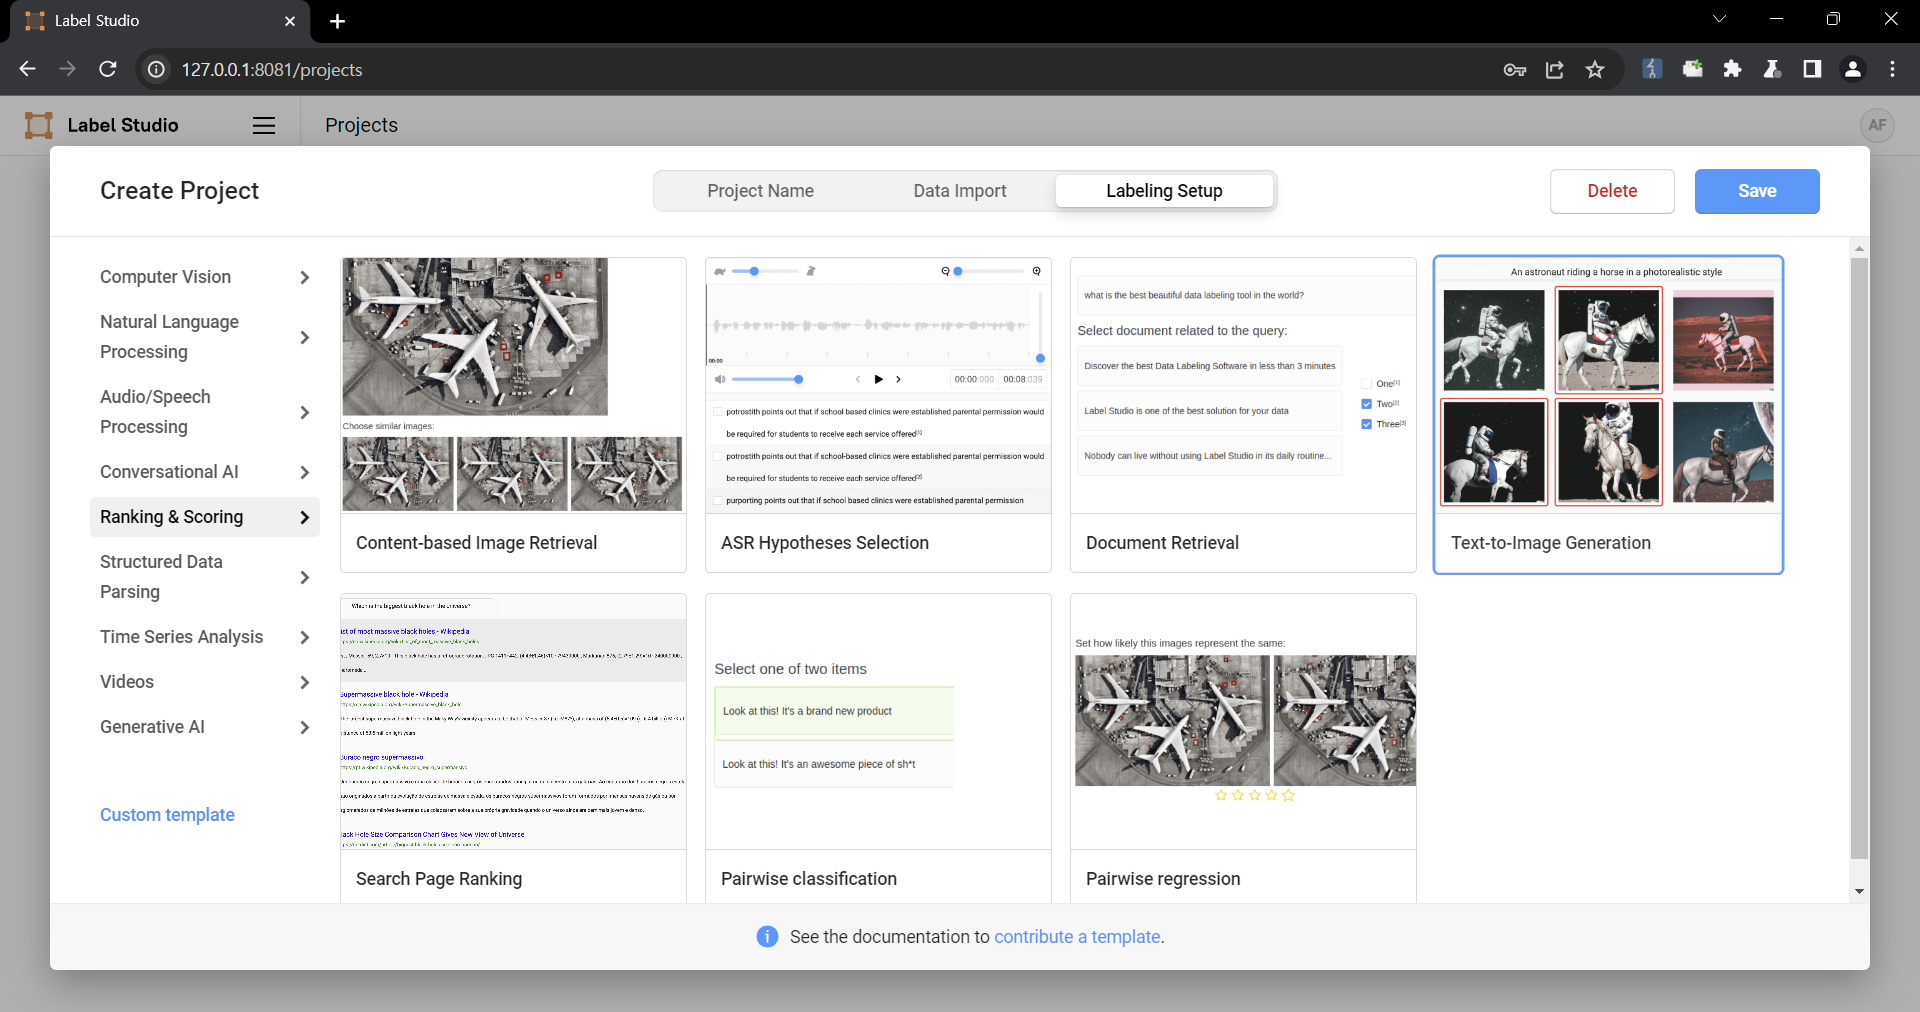\n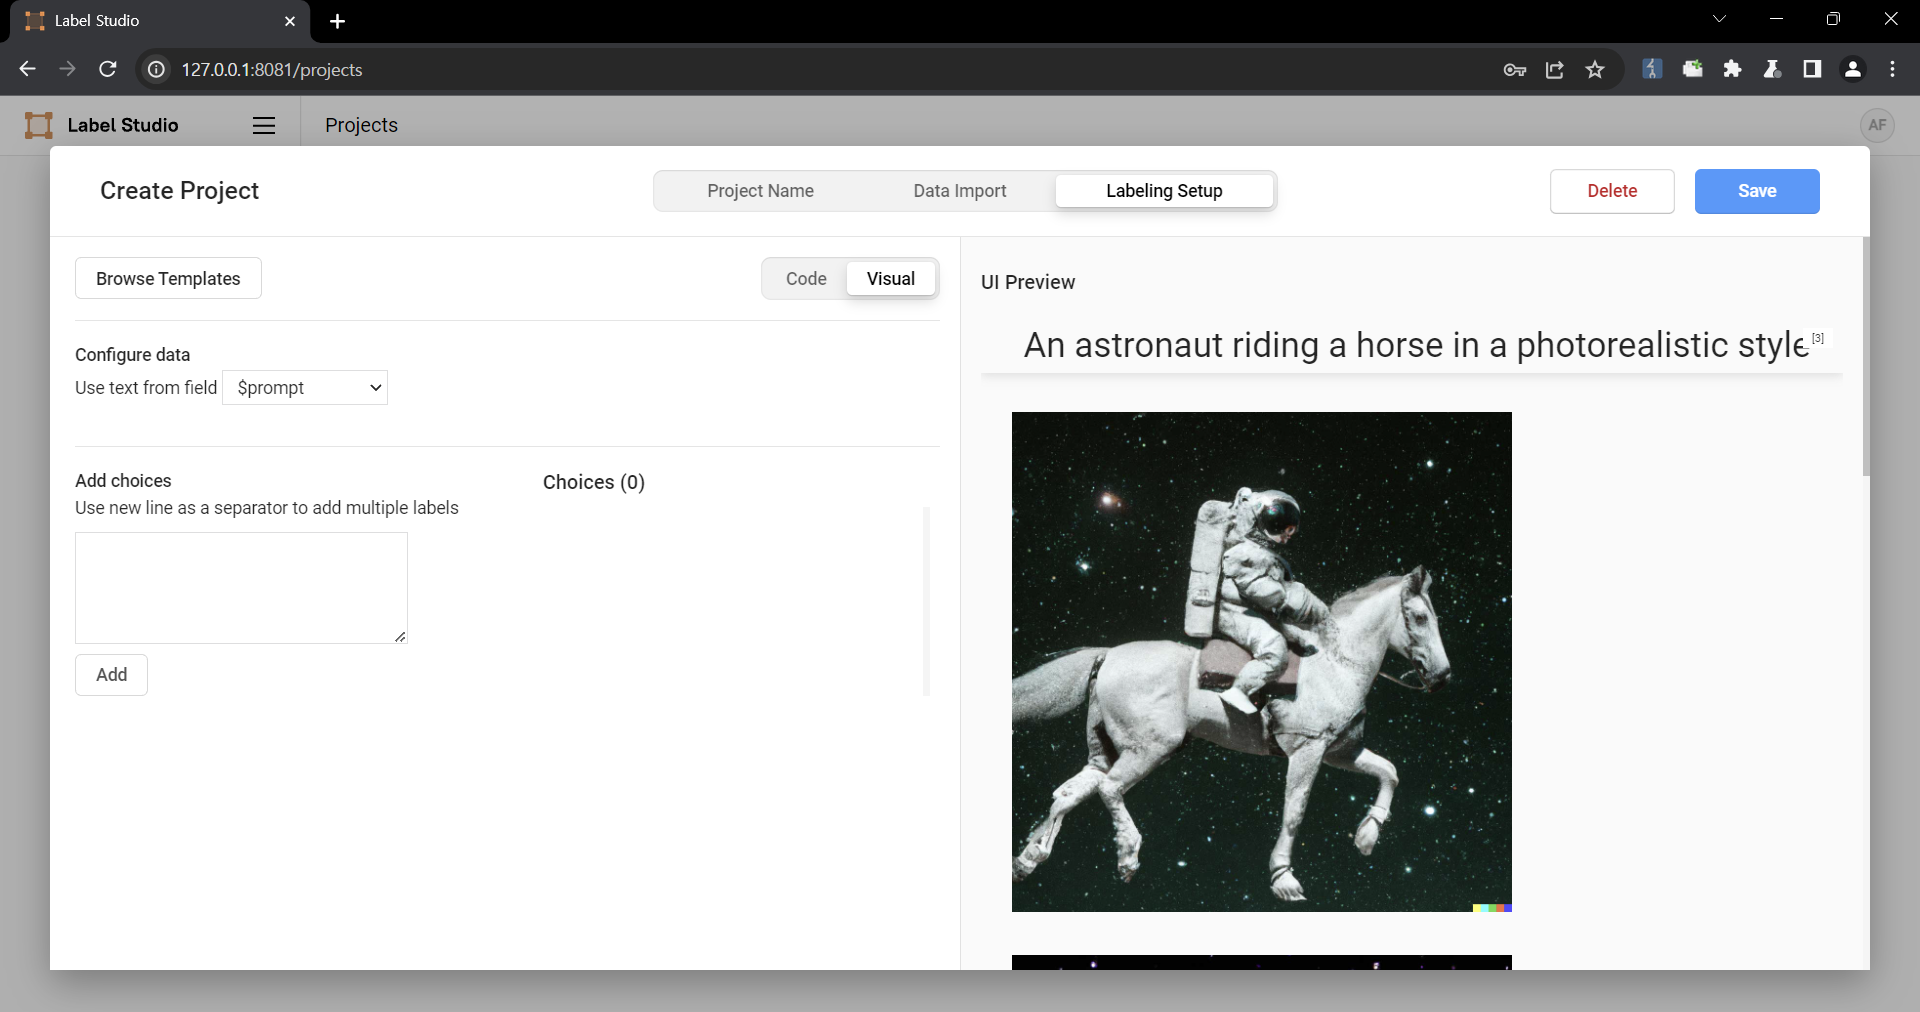\n\n4. Select a task\n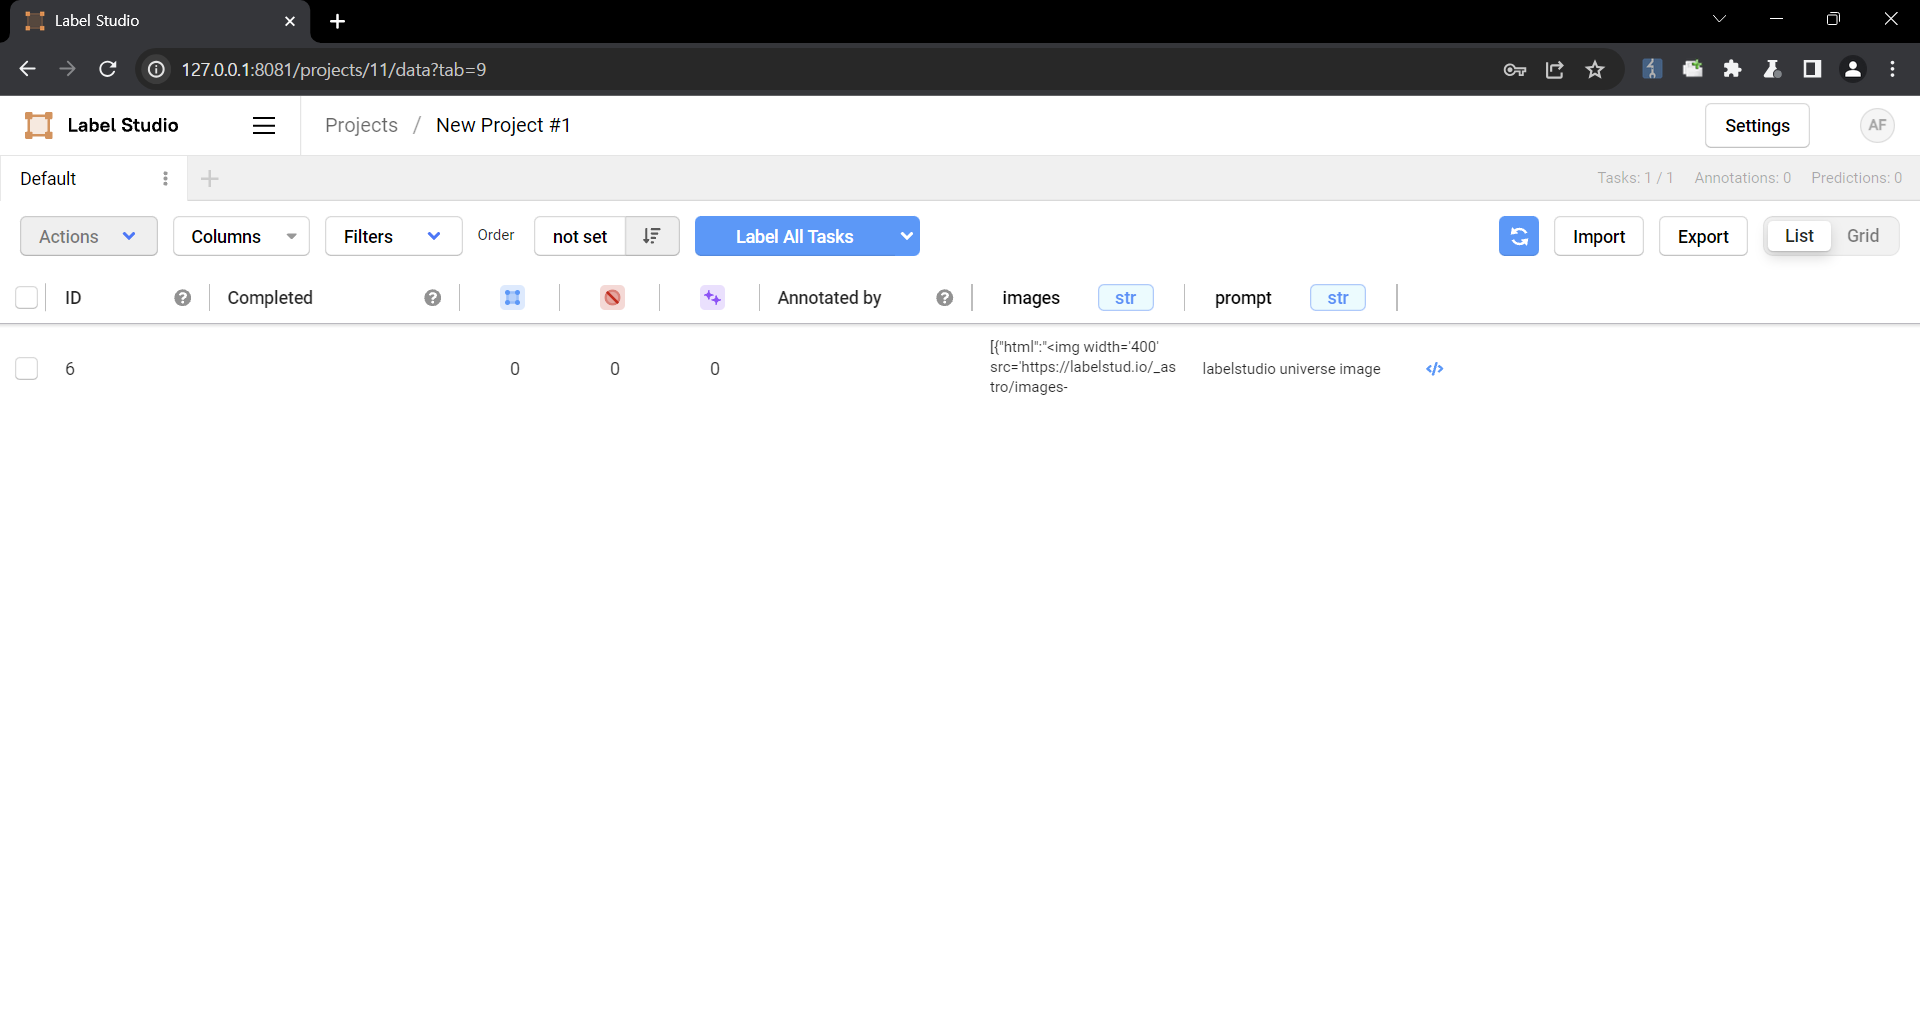\n\n5. Check that the script is running\n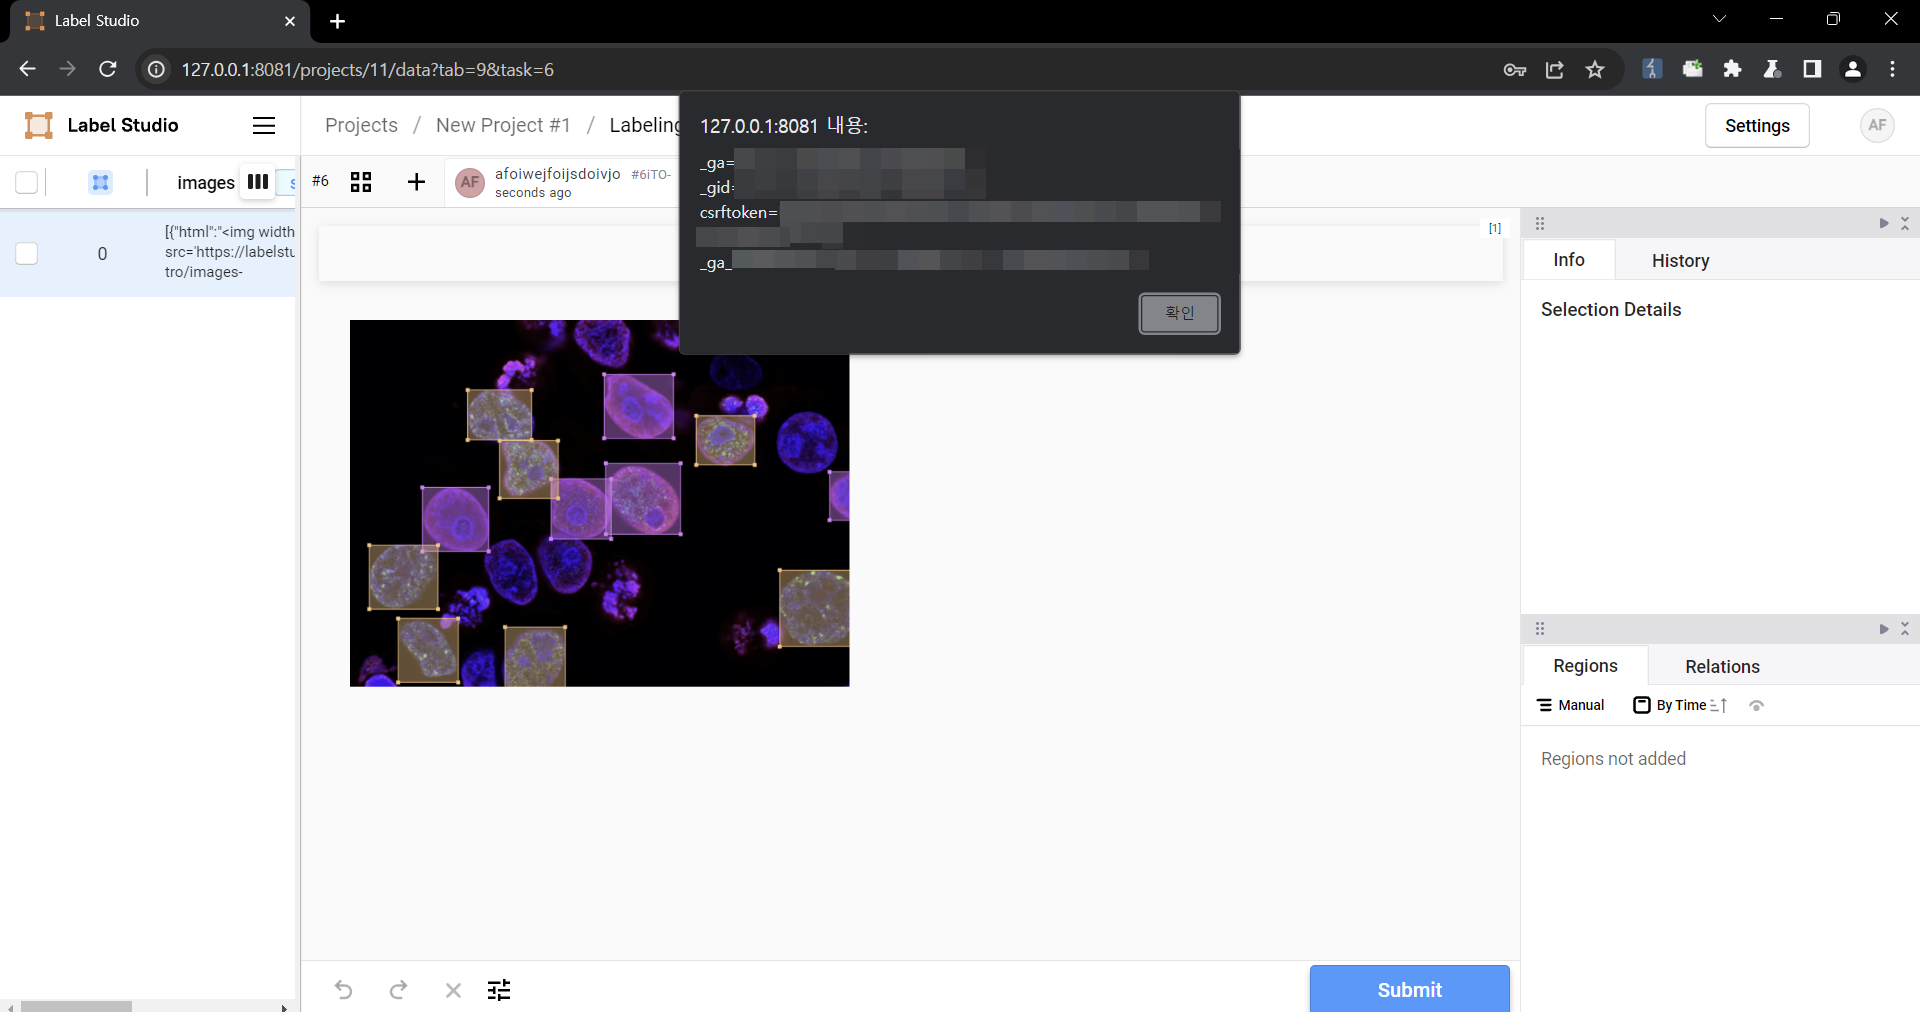\n\n### Impact\nMalicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.","cvss_v4":null,"cvss_v3":{"version":"3.1","vector":"CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N","score":6.1},"cwes":["CWE-79"],"references":["https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8","https://github.com/HumanSignal/label-studio/pull/5232","https://github.com/HumanSignal/label-studio/releases/tag/1.11.0","https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg","https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8"],"products":["humansignal:label_studio"],"source":"nvd","synced_at":"2026-10-19T21:45:59.823092188+00:00"},"epss":{"cve":"CVE-2024-26152","score":0.02217,"percentile":0.82651,"date":"2026-10-31"},"kev":null,"osv":[{"id":"GHSA-6xv9-957j-qfhg","url":"https://osv.dev/vulnerability/GHSA-6xv9-957j-qfhg","summary":"Label Studio vulnerable to Cross-site Scripting if `` or `` are used in labeling config ","modified":"2026-06-10T17:14:16.370035786Z","packages":[{"ecosystem":"PyPI","name":"label-studio","purl":"pkg:pypi/label-studio","ranges":["<1.11.0"],"fixed":["1.11.0"]}]},{"id":"PYSEC-2024-249","url":"https://osv.dev/vulnerability/PYSEC-2024-249","summary":"","modified":"2026-06-10T17:14:17.679045024Z","packages":[{"ecosystem":"PyPI","name":"label-studio","purl":"pkg:pypi/label-studio","ranges":["<1.11.0"],"fixed":["1.11.0"]}]}],"attribution":["This product uses the NVD API but is not endorsed or certified by the NVD.","EPSS scores: FIRST Exploit Prediction Scoring System, https://www.first.org/epss","Known exploited vulnerabilities: CISA Known Exploited Vulnerabilities Catalog, https://www.cisa.gov/known-exploited-vulnerabilities-catalog","Package advisories: OSV (https://osv.dev), from the GitHub Advisory Database, PyPA, Go, RustSec and other ecosystem databases, under CC-BY 4.0 or CC0","CVE records: the CVE Program's CVE List (https://www.cve.org), under its terms of use (https://www.cve.org/Legal/TermsOfUse). CVE is a registered trademark of The MITRE Corporation; this product is not affiliated with the CVE Program."]}